


Recent changes in NetApp Console


 Suggest changes

 PDFs

Learn about the most recent changes to the features and data services that are part of the NetApp Console. For a complete release history, go to the full set of release notes for each individual service.

|
The following services have been deprecated:
|
18 November 2026
Cloud Volumes ONTAP
Separate PAYGO listing for Cloud Volumes ONTAP in AWS Marketplace
NetApp now offers a separate pay-as-you-go (PAYGO) listing for Cloud Volumes ONTAP in AWS Marketplace through NetApp Standalone Listing (NSL). NetApp previously introduced the Standalone Cloud Volumes ONTAP subscription to accommodate changes to the AWS Enterprise Discount Program (EDP). The PAYGO listing is now available under the same NSL offering alongside the Cloud Volumes ONTAP annual contract, making it easier to track PAYGO usage, monitor spillover charges, and manage consumption costs.
Both the Cloud Volumes ONTAP annual contract and the PAYGO listing remain separate from the NetApp Intelligence Services (NIS) annual contract and PAYGO listings, enabling separate billing for Cloud Volumes ONTAP capacity and data services.
17 November 2026
Console setup and administration
Console agent 4.13.0
The 4.13.0 release supports both standard mode and restricted mode.
This release of the Console agent includes security improvements and bug fixes as well as the following new feature. When you upgrade a vCenter-deployed Console agent to 4.13.0 by using an ISO, ensure that the VM is restarted after the upgrade finishes. The VM might restart automatically.
Create the AWS deployment role automatically when you deploy a Console agent
You no longer need to create the IAM role for deploying a Console agent in AWS before you start. The NetApp Console can create the role for you. Learn how to deploy a Console agent in AWS from the Console
NetApp Console administration
This release includes security improvements and bug fixes as well as the following new feature.
Assign the Cloud Volumes ONTAP contributor role
You can now assign the Cloud Volumes ONTAP contributor role to give members broad access to manage Cloud Volumes ONTAP systems without letting them delete systems, volumes, aggregates, or replication relationships. Learn more about role-based access for Cloud Volumes ONTAP.
Cloud Volumes ONTAP
New Cloud Volumes ONTAP contributor role
NetApp adds the Cloud Volumes ONTAP contributor role, which has more permissions than the operator role but fewer than the admin role. A user with the operator role can perform several day-to-day workflows, including SnapMirror replication tasks. The admin role covers these workflows but also lets admin users delete Cloud Volumes ONTAP systems, which many organizations don't want for operational users. This role is important because the Console doesn't support multi-admin verification (MAV) at present, without which, an admin user can perform sensitive operations, such as deleting systems, without a second approval. The contributor role lets users perform most critical operations, such as creating systems, managing replication, and managing storage, while preventing system deletions.
The contributor role includes all operator permissions including additional capabilities to:
-
Create Cloud Volumes ONTAP systems
-
Update system settings, such as changing the instance type or upgrading the ONTAP version
-
Manage replication, including breaking, resyncing, reverse resyncing, and editing replication schedules and transfer rates
-
Manage storage, such as adding aggregates and increasing capacity
A user with the contributor role can't perform these tasks:
-
Delete systems, volumes, aggregates, or replication relationships
-
Turn systems on or off
-
Set a password
-
Access ONTAP System Manager
You assign the contributor role from Administration > Identity, the same way you assign the other Cloud Volumes ONTAP roles to users.
Microsoft Entra ID hybrid user authentication for SMB (public preview)
Cloud Volumes ONTAP 9.19.1 and later support hybrid user authentication with Microsoft Entra ID for accessing SMB shares.
Previously, Cloud Volumes ONTAP supported SMB authentication only for domain users, which required on-premises Active Directory (AD) setup. With hybrid user authentication, you can extend SMB authentication to cloud through Microsoft Entra ID, while continuing to use your existing on-premises AD infrastructure.
With hybrid user authentication, users are created in on-premises AD and synchronized to Microsoft Entra ID using Microsoft Entra Connect. ONTAP authenticates users accessing SMB shares by communicating with both on-premises AD and Microsoft Entra ID.
This feature is available as a public preview. Configuration is supported through the ONTAP CLI only. NetApp Console integration is not yet available.
16 November 2026
Ransomware Resilience
MetroCluster support
Ransomware Resilience now supports MetroCluster, enabling ransomware protection, detection, and recovery for mirrored MetroCluster configurations. When enabling ransomware protection on MetroCluster configurations, both systems in the MetroCluster pair must be added to the Console. When you discover and enable protection on one side of the pair, it's automatically enabled on the other side.
When recovering after a ransomware attack on a MetroCluster workload, you can currently only use a custom restore.
For more information, see MetroCluster discovery.
09 November 2026
Backup and Recovery
Hyper-V workloads enhancement
In this release, NetApp Backup and Recovery introduces the following enhancement for Hyper-V workloads:
NetApp MetroCluster support enhancements: NetApp Backup and Recovery now supports protecting Hyper-V hosts in a NetApp MetroCluster configuration before and after switchover or switchback operations.
For more information about protecting Hyper-V hosts in a NetApp MetroCluster configuration, refer to Discover and manage Hyper-V workloads.
For details about protecting Hyper-V workloads, refer to Learn about protecting Hyper-V workloads with NetApp Backup and Recovery.
Disaster Recovery
Job monitoring enhancement when rerunning jobs
If you rerun certain failed, canceled, or timed-out operations, NetApp Disaster Recovery now registers these operations as new jobs and identifies the user who initiated the action. Previously, Disaster Recovery listed new jobs under the initial job. This enhancement creates a more visible audit trail for jobs in Disaster Recovery as long as the request hasn't been redacted. It applies only to discovery, resync, compliance, protection, replication plan, and backup retention jobs. Rerun failback, failover, and migration operations aren't listed as new jobs. Only the latest job in a rerun chain qualifies, and at most one rerun can be queued behind a running one.
For more information, see Monitor jobs in Disaster Recovery.
Ransomware Resilience
Managed blocked file extensions
Ransomware Resilience now provides the capability to customize the list of allowed or blocked file extensions on a workload when you've enabled the Block suspicious file extensions protection option. With this enhancement, you can configure the workload to only allow specific file types on the storage VM (SVM) or to block specific file extensions. This enhancement supports more granular control over the file extension option and also allows you to create different lists for different SVMs.
For more information, see Manage blocked file extensions in Ransomware Resilience.
02 November 2026
Cloud Volumes ONTAP
Guidance for upgrading ONTAP hotfixes for specific Cloud Volumes ONTAP versions
ONTAP has released the following hotfixes compatible with Cloud Volumes ONTAP versions 9.12.1, 9.13.1, 9.14.1, 9.15.1, 9.16.1, 9.17.1, 9.18.1, and 9.19.1:
-
9.12.1P20HF1
-
9.13.1P21HF1
-
9.14.1P18HF1
-
9.15.1P20HF1
-
9.16.1P16HF1
-
9.17.1P11HF1
-
9.18.1P8HF1
-
9.19.1P3HF1
For details, refer to NTAP Security Advisory 20261021-0021.
For your Cloud Volumes ONTAP systems, you might be prompted to upgrade to these hotfixes in the NetApp Console. However, these hotfixes are supported only when the Console agent version is 4.12.0 or later. If the Console agent version is earlier than 4.12.0, ignore the prompt.
01 November 2026
Workload Factory
Workload Factory administration enhancements
Check and refresh custom dashboard data
You can now see when your custom dashboard metrics were last updated and manually refresh them. Hover over Refresh data to view the last Updated date and time.
Select Refresh data to start a new scan. A banner confirms that the scan has started, and the button is disabled until the scan finishes.
When new data is available, select Load it now in the notification banner to update the dashboard.
Both Refresh data and Load it now create data collection events in Tracker.
Specify regions for custom dashboards
Custom dashboards now ask you to choose one or more regions if your request does not include them. Dashboard data is limited to the regions you select.
IAM policy for FSx for ONTAP link creation
The CloudFormation template and Terraform code for creating links now use an IAM policy instead of inline Lambda permissions.
Audit and tracking for AI agent actions
You can now use Tracker to review changes to AI agent settings and, in read/write mode, each approval request, including the agent's question and the user's answer.
Resource changes made through Workload Factory APIs are logged by the Workload Factory service that performs the operation.
Amazon FSx for NetApp ONTAP enhancements
Initiator group diagram enhancements
The diagram that displays initiator groups for block devices on the Manage Client Access page now includes more details for hosts. When you hover over a host in the diagram, host details appear, including the host name, instance ID, workload type, region, and iSCSI Qualified Name (IQN).
Email enhancement for well-architected issues
The new email design provides more details and context for configuration issues detected by Workload Factory. The email includes the number of analyzed resources, how many have warning or critical issues, and what those issues are. The email also links to the FSx for ONTAP well-architected dashboard so you can address issues right away.
Well-architected dashboard enhancements
Support for selected configuration checks
You can manually run analysis on selected configurations so that you analyze only the configurations you're interested in and reduce wait time.
New recommendations in the well-architected analysis
Workload Factory now includes the following configurations in the well-architected analysis for FSx for ONTAP file systems:
For storage workloads:
-
Connect host to failover node: checks whether hosts are connected to the failover node in an active-passive FSx for ONTAP file system for reliability.
-
Connect host to preferred node: checks whether hosts are connected to their block devices using the preferred node for performance efficiency.
-
ARP/AI multi-device detection gap: ARP/AI provides full protection coverage when a volume has only one block device attached to it. If a volume has multiple block devices attached, Workload Factory moves the block devices to new volumes so that each volume has only one block device.
-
Clone cleanup: checks whether there are any volume clones older than 30 days that can be deleted to optimize storage usage and reduce costs.
-
Match igroup OS to host: checks whether the operating system of the initiator group (igroup) matches the host's operating system to prevent I/O or performance issues.
For Kubernetes workloads:
-
QoS configuration: checks whether Kubernetes persistent volumes are protected with an ONTAP QoS policy for performance efficiency.
-
Dedicated Kubernetes storage VM: checks whether the file system is using a dedicated storage VM for Kubernetes workloads to improve isolation and simplify storage management.
-
Dedicated Kubernetes export policy: checks whether each Kubernetes persistent volume has a dedicated export policy that only allows access from the cluster's worker nodes.
-
Bidirectional CHAP for Kubernetes iSCSI backends: checks whether Trident iSCSI backends have mutual CHAP authentication enabled for security.
-
Disable
showmounton the application storage VM: checks whethershowmountis disabled on the application storage VM to prevent clients from listing exports they can't access.
For database workloads:
-
SAP HANA snapshot policy: checks whether the snapshot policy is set to "None" for SAP HANA volumes to lower storage costs and improve performance for active database data.
-
MySQL snapshot policy: checks whether the snapshot policy is set to "None" for MySQL volumes to lower storage costs and improve performance for active database data.
-
PostgreSQL snapshot policy: checks whether the snapshot policy is set to "None" for PostgreSQL volumes to lower storage costs and improve performance for active database data.
Current and recommended values for configurations
You can view the current and recommended values for some unoptimized configurations in the well-architected dashboard. This tells you what the recommended value is before you fix it.
-
Cold data tiering
-
Snapshot policy
-
SSD capacity headroom
Cost improvements
Cost forecasting and insights
You can now forecast costs for your FSx for ONTAP file systems using the cost forecasting feature. This helps you plan your budget and optimize your resources effectively. You can also view insights about your costs and usage patterns to identify opportunities for cost optimization.
AWS Cost and Usage Reports (CUR)
Workload Factory now uses AWS Cost and Usage Reports (CUR) instead of AWS Cost Explorer to provide detailed billing records delivered to customer-owned S3 buckets. CUR offers better cost granularity and serves as the foundation for advanced FinOps, chargeback, and cost allocation use cases.
Storage VM migration improvements
Workload Factory provides enhanced guidance within the user interface for migrating storage VMs. This includes step-by-step instructions and a test run before committing the migration to production.
Replication lag email notification improvement
When a large number of related replication lag events occur, Workload Factory automatically consolidates them into a single email notification so you won't get overwhelmed by notifications.
Automatic capacity management enhancement
You can now turn on automatic capacity management notifications to try out the feature before asking Workload Factory to manage your capacity automatically. You'll be notified when your file system is running low on capacity.
Database configurations included in well-architected dashboard
The well-architected dashboard now includes recommendations for your database configurations, allowing you to assess and optimize your setup based on best practices. The first configurations included in the dashboard are:
-
Cold data tiering
-
Storage efficiencies
-
Snapshot policy
-
SSD capacity headroom
-
Block device space management
-
OS type
-
Match block device OS type to host
-
Inactive block devices (LUNs)
-
Data files (.mdf) placement
-
Log files (.ldf) placement
-
Multipath I/O status
-
Multipath I/O timeout
-
Cluster quorum
-
Compute rightsizing
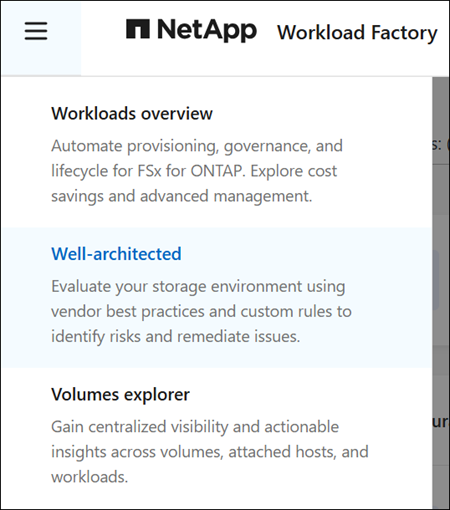
Select the main menu in the Workload Factory console, and then select Well-architected to find the well-architected dashboard.
Throughput decision points
You can now see client throughput recommendations and automation decision points. Hover over a decision point to view details, such as the current and recommended SKU or breached metrics in time window (%).
Workload Factory for VMware enhancements
These enhancements cover the EVS TCO calculator for VMware migrations.
Support for i7i.metal-24xl and i7i.metal-48xl instances in the EVS TCO calculator
The EVS TCO calculator now supports AWS i7i.metal-24xl and i7i.metal-48xl EC2 instances as cluster hosts. Compared to i4i.metal configurations, i7i.metal-24xl instances lower the EVS starting cost by about 33% for compute and 25% for vSAN storage.
The calculator compares all instance types and automatically selects the lowest-cost option. A new comparison section displays EVS host configurations side by side, making it easier to choose the best setup for your needs.
Workload Factory for EDA enhancements
These enhancements cover volume details in latency analysis, a file system pressure check, throughput decision points, and running a latency analysis again.
View volume details during latency analysis
You can view more volume details in Workload Factory while you analyze a latency event so that you can see how the volume is configured. The Detailed latency analysis page shows Volume type (RW or DP) and Volume style (FlexVol or FlexGroup).
Check file system pressure for a latency event
In Workload Factory, you can check whether file system pressure affected performance when a latency event occurred so that you can decide whether to investigate the file system. For a volume with a latency alert, you can view CloudWatch data from the 40 minutes before the event and open the file system to investigate further.
Review throughput decision points for EDA
You can review client throughput decision points on the EDA Overview dashboard so that you can see when Workload Factory recommended or applied a throughput change. Hover over a decision point to view details, such as the current and recommended SKU or the breached metrics in the time window.
Run a latency analysis again
You can run a latency analysis again in Workload Factory for a volume so that you can refresh the results after you investigate or make a change. Select Run analysis again to start a new analysis and update the results.
Google Cloud NetApp Volumes enhancements
View Google Cloud NetApp Volumes storage pools
You can now view your Google Cloud NetApp Volumes storage pools in NetApp Workload Factory. Filter by projects, credentials, and region, and select a storage pool's name to view its full details, including zone, replica zone, throughput, description, and labels.
OCI NetApp Storage Service enhancements
Well-architected analysis for OCI NSS systems
NetApp Workload Factory includes the well-architected assessment for OCI NSS systems. The assessment provides insights, recommendations, and fixes to help you achieve operational excellence.
Configuration assessments are available for the following pillars of the OCI Well-Architected Framework:
-
Reliability: file object capacity, snapshot policy, and SSD capacity headroom
-
Operational excellence: host-visible capacity reporting and volume capacity headroom
-
Cost optimization: cold data tiering, snapshot cleanup, and storage efficiencies
Learn more about the well-architected analysis for OCI NSS systems and about implementing well-architected configurations.
26 October 2026
AI Data Engine
AI Data Engine 1.3
AI Data Engine is a metadata intelligence service, managed through NetApp Console, that scans your connected systems, builds a metadata catalog, and gives you the visibility and tools to optimize storage and govern data at scale. You can deploy AI Data Engine as an AIDE single-node deployment, or as an AIDE multi-node deployment if your environment requires Kubernetes-based high availability at large scale.
AI Data Engine 1.3 is the first generally available (GA) release.
- Deploy at the scale your environment requires
-
Choose an AIDE single-node deployment for a fast start on a single VM, or an AIDE multi-node deployment on your own Kubernetes cluster for high availability and larger scale. If your environment requires a proxy to reach the internet, learn about proxies for AIDE and deploy with a proxy.
- Bring your data into scope
-
Connect file shares, database servers, and StorageGRID systems, and choose which data resources to scan.
- Keep scanning healthy
-
Monitor your deployment's health to identify the issues that could interrupt scanning, and gather the details you need to resolve them.
- Recover storage capacity
-
Identify cold, stale, and duplicate data across your connected systems based on your configured thresholds, and see which systems and data owners hold the highest concentrations of this data.
- Define cold and stale data for your organization
-
Set the thresholds that determine which data is classified as cold or stale to match your retention policies.
- Identify who to contact about data
-
Identify which data owners hold the highest concentrations of cold, stale, or duplicate data from the dashboard. Then filter by owner or group in the investigation view to review results and find out who to contact.
- Reduce cost and risk
-
Filter across all connected systems by access time, modification date, creation date, file size, duplicate status, and other criteria to find files that meet your organization's data management goals. Act on results directly or save criteria as a policy.
- Eliminate duplicate data
-
Find files that have duplicate copies across your connected systems. Filter by the Duplicates attribute or by file hash to review duplicate groups, then clean up the duplicate copies.
- Find access risks
-
Identify directories with open permissions so that you can prioritize them for a permissions review.
- Investigate structured data
-
Find oversized or unused database tables across your connected database servers.
- Reduce storage costs
-
Enforce your organization's data lifecycle policies by copying and archiving files to NFS or SMB destinations, tagging items for tracking, or permanently deleting files according to your retention requirements.
- Monitor data conditions continuously
-
Save filter criteria as named policies to track recurring data conditions over time, such as cold or oversized files, and receive notifications when the impacted file count changes.
- Give AI clients governed access to your metadata
-
Connect Claude Code, Claude Desktop, Cursor, or OpenCode to AI Data Engine through the Model Context Protocol (MCP). Enable the collections that AI clients can search, and use Microsoft Entra ID scopes to control who can search each collection. AI clients can search metadata and tag files.
- Assign admin and viewer roles
-
Control who can investigate data and take actions by assigning the AI Data Engine administrator or viewer role to users in your organization.
Backup and Recovery
Kubernetes workloads enhancements
In this release, NetApp Backup and Recovery introduces the following enhancements for Kubernetes workloads:
-
Trident Protect 26.10: This release includes Trident Protect 26.10.
-
ontap-nas-economy and ontap-san-economy driver support: You can now protect persistent volume claims (PVCs) provisioned by the NetApp Trident
ontap-nas-economydriver (Qtrees) and theontap-san-economydriver (LUNs). When you protect PVCs using economy drivers, the entire underlying FlexVol or LUN is protected. You can restore individual PVCs from these backups. -
Kubernetes-aware alerting: Alerts are now sent once per Kubernetes application instead of once per volume.
-
Volume group snapshot support: You can now create volume groups when defining a Kubernetes application. Volume groups enable you to snapshot multiple volumes together as a crash-consistent set, ensuring data consistency across all volumes in the group.
-
S3-compatible object storage support: You can now back up Kubernetes application resources and data to S3-compatible object storage by adding backup target credentials and configuring protection policies.
For details about protecting Kubernetes workloads, refer to Learn about protecting Kubernetes workloads with NetApp Backup and Recovery.
ONTAP Volumes workloads enhancements
In this release, NetApp Backup and Recovery introduces the following enhancements for ONTAP Volumes workloads:
-
Protection reports: NetApp Backup and Recovery now supports creating and downloading expanded reports for ONTAP Volumes workloads.
-
Retain backups when unregistering an ONTAP system: When you unregister an ONTAP system from NetApp Backup and Recovery, you can now choose to either discard the previously backed up data or keep it available for restoration. NetApp Backup and Recovery documentation now includes instructions for using the ONTAP CLI to restoring the retained data after the system is unregistered.
For more details, refer to Unregister Backup and Recovery for a system.
For details about protecting ONTAP Volumes workloads, refer to Learn about ONTAP volume protection with NetApp Backup and Recovery.
Oracle Database workloads enhancement
In this release, NetApp Backup and Recovery introduces the following enhancement for Oracle Database workloads:
Restore to an alternate location: NetApp Backup and Recovery now supports restoring an Oracle database to an alternate location (a different registered host).
For details about protecting Oracle Database workloads, refer to Learn about protecting Oracle Database workloads with NetApp Backup and Recovery.
Ransomware Resilience
New manual workflow for creating a user activity agent
Ransomware Resilience now provides a manual user activity agent creation workflow, enabling more control in how you create your user activity agent on your VM. With this new workflow, you can install the user activity agent directly and configure proxy settings without providing VM SSH keys.
For more information, see Create a user activity agent.
20 October 2026
Ransomware Resilience
Enhanced isolated recovery environment configuration
Ransomware Resilience now provides an enhanced isolated recovery environment configuration workflow. The new workflow clarifies and simplifies the process to set up an isolated recovery environment for cloud or on-premises environments.
For more information, see Create an isolated recovery environment for a clean restore.
Improved workflow for enabling user activity monitoring
Ransomware Resilience has improved the workflow for enabling user activity monitoring. Previously, Ransomware Resilience tested the connection of the data collector every time you enabled a ransomware protection strategy with user activity monitoring on a workload. With that update, Ransomware Resilience now skips that check if a data collector exists for the storage VM and is in the "running" state, which accelerates the protection workflow.
For more information, see protect workloads.
Google Cloud NetApp Volumes Flex service level generally available
Support for the Flex service level from Google Cloud NetApp Volumes in Ransomware Resilience is now generally available (GA).
19 October 2026
Backup and Recovery
Oracle Database workloads enhancement
In this release, Oracle Database workloads introduces the following enhancement:
Oracle Data Guard support: NetApp Backup and Recovery now supports using protection groups to protect primary and standby databases that use Oracle Data Guard for high availability.
For details about protecting Oracle Database workloads, refer to Learn about protecting Oracle Database workloads with NetApp Backup and Recovery.
15 October 2026
Console setup and administration
Console agent 4.12.0
The 4.12.0 release supports both standard mode and restricted mode.
This release of the Console agent includes security improvements and bug fixes.
NetApp Console administration
This release includes security improvements and bug fixes.
Digital advisor
E-Series and StorageGRID support in Value Insights
Value Insights now includes ONTAP, E-Series, and StorageGRID systems in health, risk, security risk, and lifecycle totals. You can filter the dashboard by platform to view platform-specific details. Delivered and projected savings remain available for ONTAP systems only.
14 October 2026
Cloud Volumes ONTAP
Cloud Volumes ONTAP 9.19.1 in Azure
You can now use the NetApp Console to deploy and manage the General Availability (GA) version of Cloud Volumes ONTAP 9.19.1 in Azure.
The Console has supported Cloud Volumes ONTAP 9.19.1 in AWS and Google Cloud since August 2026.
Azure encryption at host for Cloud Volumes ONTAP
Starting with Cloud Volumes ONTAP 9.19.1 GA, Azure encryption at host is enabled by default for new Azure single-node and high availability (HA) deployments that meet the prerequisites. This feature encrypts data on the physical server that hosts the VM, including the ephemeral disk and associated host-level caches, as data is written to and read from the host.
Before deploying Cloud Volumes ONTAP in Azure, confirm that your environment meets the following prerequisites:
-
The
EncryptionAtHostfeature is registered for your Azure subscription. Refer to Microsoft documentation: Enable encryption at host. -
Your selected VM instance type supports encryption at host in your Azure region. Refer to Microsoft documentation: Finding supported VM sizes.
Note these points:
-
No additional configuration is required.
-
If these prerequisites aren't met, Azure encryption at host is not enabled for your Cloud Volumes ONTAP deployment.
-
Encryption at host applies only to Azure, not to AWS or Google Cloud.
Microsoft documentation: Use the Azure portal to enable end-to-end encryption using encryption at host
Backend network encryption on Cloud Volumes ONTAP clusters in Azure and Google Cloud
Cloud Volumes ONTAP 9.19.1 and later support backend cluster network encryption for HA configurations in Azure and Google Cloud.
Enabling cluster network encryption might affect cluster performance. Exercise caution and verify that your environment can accommodate the additional overhead before enabling this feature.
Ability to reduce disruptions during Azure scheduled maintenance
During scheduled maintenance, Azure can briefly pause a VM in a Cloud Volumes ONTAP HA pair. ONTAP might interpret the pause as a node outage and move storage operations to the partner node, then move them back when the VM resumes (takeover and giveback). This process can disrupt active client connections even when there is no node failure.
With Cloud Volumes ONTAP 9.19.1 and later, you can enable an optional setting that lets the HA pair continue operating through an Azure scheduled-maintenance freeze without automatically initiating takeover and giveback.
|
|
This feature is available as a public preview with Cloud Volumes ONTAP 9.19.1. |
12 October 2026
Backup and Recovery
General NetApp Backup and Recovery enhancement
In this release, NetApp Backup and Recovery introduces the following licensing enhancement for all workloads:
Licensing change: Charges no longer apply to backups using disk-to-disk or disk-to-disk fan-out architectures. Charges apply only to backups to object storage, including backups using 3-2-1 or disk-to-object-storage architectures.
For details about licensing, refer to Set up licensing for NetApp Backup and Recovery.
Hyper-V workloads enhancements
In this release, Hyper-V workloads introduces the following enhancements:
-
NetApp MetroCluster support: NetApp Backup and Recovery now enables you to protect Hyper-V VMs mirrored by NetApp MetroCluster.
-
Spanning disk protection for SAN VMs: For CIFS and SAN configurations, you can now protect every disk attached to each VM in a protection group. This includes files distributed across multiple ONTAP volumes or ONTAP storage systems (spanning disks) and files limited to a single location.
For details about protecting Hyper-V workloads, refer to Learn about protecting Hyper-V workloads with NetApp Backup and Recovery.
Oracle Database workloads enhancement
In this release, Oracle Database workloads introduces the following enhancement:
Automatic archive log management: During database restore and clone operations, NetApp Backup and Recovery automatically discovers and mounts the required archive logs, then unmounts them when the operation is complete. Primary, secondary, and object storage log sources are supported.
For details about protecting Oracle Database workloads, refer to Learn about protecting Oracle Database workloads with NetApp Backup and Recovery.
Disaster Recovery
Optional boot order for Kubernetes resource groups
NetApp Disaster Recovery now supports setting optional boot order for resource groups in a Kubernetes replication plan by specifying a priority order and optional delay time for resources. This option enables you to boot resources at the same time when necessary and delay booting for resources that are dependent on others, supporting your applications to come back online in a healthy manner.
For more information, see create a replication plan.
SnapLock volume support
Disaster Recovery now supports SnapLock volumes, enabling you to failover tamperproof snapshots.. When performing failback with SnapLock volumes, you must use the Take snapshot now option to ensure failback completes successfully.
Simplified refresh and compliance runs
Refresh runs for vCenter, replication plans, and compliance have been simplified into a single job to facilitate a faster execution. To see this change, learn how to monitor jobs.
Kubernetes compliance checks
Disaster Recovery has added compliance checks to identify missing working environments for Kubernetes workloads. These compliance checks help ensure workload health for the integrity of your replication plans.
Keystone
This Keystone STaaS release includes the following updates in the Keystone dashboard in the NetApp Console.
Generate health insights for Keystone subscriptions
You can download on-demand PowerPoint reports or schedule one-time, weekly, monthly, or quarterly delivery from Storage > Keystone > Monitoring > Health reports in the NetApp Console. Each report combines subscription usage, operational health, risks, and vulnerabilities across selected subscriptions, helping you identify concerns and share actionable insights with recipients. To learn more, refer to Generate and schedule health reports for Keystone subscriptions.
View ONTAP cluster and aggregate capacity
You can view physical capacity, logical capacity, and storage efficiency for ONTAP clusters and their aggregates in Assets > Clusters and aggregates. This is available only for Keystone STaaS subscriptions billed on physical capacity. To learn more, refer to View assets across your Keystone subscriptions and View assets associated with a Keystone subscription.
30 September 2026
Workload Factory
Initial release of Oracle Cloud Infrastructure NetApp Storage Service for Workload Factory
The initial release of OCI NetApp Storage Service (OCI NSS) for Workload Factory offers onboarding, system discovery, credential management, and link creation and association. To request access to OCI NSS, open a support ticket with Oracle.
Workload Factory documentation for NetApp Console users
You can find detailed documentation for Workload Factory in the NetApp Console, including guides for onboarding, system discovery, credential management, and link creation and association.
28 September 2026
Backup and Recovery
General NetApp Backup and Recovery enhancement
In this release, KVM, Hyper-V, and VMware workloads introduce the following enhancement:
Console Role-Based Access Control (RBAC) support: The Hyper-V, KVM, and VMware workloads now support the NetApp Console framework for RBAC, enabling you to manage access to individual Hyper-V, KVM, or VMware hosts.
ONTAP Volumes workloads enhancements
In this release, ONTAP Volumes workloads introduces the following preview enhancements:
-
Cloud Volumes ONTAP Azure Entra ID support: You can now use Microsoft Entra ID authentication for Azure object storage bucket configurations if you don't want to use the storage account access key for Azure authentication. This option is supported for Cloud Volumes ONTAP in Azure systems running ONTAP 9.16.1 or later.
-
Job Monitor custom date range filtering: You can now search jobs from the past 90 days by selecting a custom start and end date from a calendar in the Job Monitor.
For details about protecting ONTAP Volumes workloads, refer to Learn about ONTAP volume protection with NetApp Backup and Recovery.
VMware workloads enhancement
In this release, VMware workloads introduces the following enhancement:
Google Cloud NetApp Volumes Flex Unified support: NetApp Backup and Recovery for VMware workloads now supports the the Flex Unified service level for Google Cloud NetApp Volumes. Flex Unified is supported in ONTAP-mode only.
For details about protecting VMware workloads, refer to Protect VMware workloads with NetApp Backup and Recovery.
25 September 2026
Digital advisor
Content update for the Value Insights Dashboard
An update to the documentation for the Value Insights Dashboard has been published.
Learn more about how to use Value Insights Dashboard in Digital Advisor.
Deprecation notice for Config Drift
The Config Drift feature has been deprecated and is no longer available in Digital Advisor as of September 2026.
For questions or to share feedback, contact the Active IQ team.
21 September 2026
Backup and Recovery
ONTAP Volumes workloads enhancements
In this release, ONTAP Volumes workloads introduces the following preview enhancements:
-
Improved support for dark sites: NetApp Backup and Recovery for dark sites now provides the same ONTAP Volumes data protection capabilities as NetApp Backup and Recovery. This enhancement includes updated backup, restore, and job-management services and a new metadata database. During an upgrade, existing database data is preserved and migrated automatically. After the upgrade, review the audit logs to verify that the migration completed successfully. NetApp Backup and Recovery for dark sites supports only ONTAP Volumes workloads.
-
Cancel volume restore jobs: You can now cancel ongoing ONTAP Volumes restore jobs from the job monitoring page, making it easier to manage long-running or slow-running jobs.
-
Improved volume indexing status reporting: The ONTAP Volumes dashboard now reports indexing status more accurately by introducing the
Not Applicablestatus for volumes and snapshot copies that are not eligible for indexing. TheNot Indexedstatus is now reserved for volumes that are waiting to be indexed, and volume details now show per-snapshot indexing status with hovertext that explains why a volume or snapshot copy will not be indexed. -
NetApp AFX support: You can now protect volumes hosted on 2- and 4-node NetApp AFX clusters.
For details about protecting ONTAP Volumes workloads, refer to Learn about ONTAP volume protection with NetApp Backup and Recovery.
Kubernetes workloads enhancements
In this release, Kubernetes workloads introduces the following enhancements:
-
Trident Protect 26.09: This release includes Trident Protect 26.09.
-
Cluster- and namespace-granular Role-Based Access Control (RBAC): During Kubernetes cluster discovery, you can control access to resources by selecting a project or folder to associate with the new cluster. You can also register specific namespaces for access control. This enables more granular access control at either the cluster or namespace level.
-
Restore files and folders: You can now restore or download specific files and folders from Kubernetes VM-based application backups.
For details about protecting Kubernetes workloads, refer to Learn about protecting Kubernetes workloads with NetApp Backup and Recovery.
Cloud Volumes ONTAP
Support for capacity-based licenses in private-mode deployments
You can now deploy Cloud Volumes ONTAP systems in private mode with capacity-based licenses in AWS, Azure, and Google Cloud.
NetApp supports only the Essentials package for capacity-based licensing in private mode. Purchase a capacity-based Bring-Your-Own License (BYOL) Essentials package from NetApp and assign it to your system during deployment. The first 500 GiB of consumed capacity does not count toward your license charges. You can purchase additional packages as your workload requirements grow.
NetApp recommends capacity-based licensing for all private-mode Cloud Volumes ONTAP deployments. If you have existing private-mode deployments with node-based licenses, you can convert them to capacity-based licensing by purchasing an Essentials package from NetApp. This new deployment capability, combined with the conversion option, supports NetApp's plan to gradually move away from node-based licensing to capacity-based licensing.
17 September 2026
Console setup and administration
Private mode release (4.10.0)
A new private mode release is now available to download from the NetApp Support Site
The 4.10.0 release includes updates to the following NetApp Console components and services.
| Component or service | Version included in this release | Changes since the previous private mode release |
|---|---|---|
Console agent |
4.10.0 |
Go to the What's new in NetApp Console page and refer to the changes included for versions 4.10.0. |
NetApp Backup and Recovery |
5.6.2 (31 August 2026) |
|
NetApp Data Classification |
1.56.0 (10 August 2026) |
Go to the what's new in NetApp Classification page. |
Private mode 4.10.0 supports Red Hat Enterprise Linux (RHEL) 9.6
Private mode can now be installed and run on Red Hat Enterprise Linux (RHEL) 9.6, providing users with the latest supported operating system for enhanced security and performance. Learn about host requirements for private mode
16 September 2026
Console setup and administration
Console agent 4.11.0
The 4.11.0 release supports both standard mode and restricted mode.
This release of the Console agent includes security improvements and bug fixes.
NetApp Console administration
Simplified agent deployment flow for Cloud Volumes ONTAP subscribers in AWS Marketplace
If you are a new subscriber to a standalone Cloud Volumes ONTAP subscription in AWS Marketplace, the NetApp Console now simplifies agent deployment. You can configure AWS roles, policies, and credentials with fewer steps, use default values automatically on a single page, and move through the setup faster.
Backup and Recovery
General NetApp Backup and Recovery enhancement
In this release, KVM, Hyper-V, and VMware workloads introduce the following enhancement:
Credential selection during VM host discovery: When you discover a KVM, Hyper-V, or VMware host, you can now use credentials that you have already added to Backup and Recovery.
Hyper-V workloads enhancement
In this release, Hyper-V workloads introduces the following enhancement:
Spanning disk protection for VMs: For CIFS configurations, Backup and Recovery now supports protecting every disk attached to each VM in a protection group. This includes files distributed across multiple ONTAP volumes or ONTAP storage systems (spanning disks) and files limited to a single location.
For details about protecting Hyper-V workloads, refer to Learn about protecting Hyper-V workloads with NetApp Backup and Recovery.
ONTAP Volumes workloads enhancement
In this release, ONTAP Volumes workloads introduces the following preview enhancement:
Daily backup data transfer report: NetApp Backup and Recovery for Volumes now includes a daily backup data transfer report under the Reports tab, giving you visibility into daily backup and replication data transfer activity across your environment. You can generate the report for the full account or for selected storage systems, filter by date range and protection type, and download the results as a CSV.
For details about protecting ONTAP Volumes workloads, refer to Learn about ONTAP volume protection with NetApp Backup and Recovery.
Disaster Recovery
Kubernetes support in NetApp Disaster Recovery is now generally available (GA)
Support for Kubernetes-based workloads in NetApp Disaster Recovery is now generally available (GA). With support for Kubernetes-based workloads, you can protect applications running on Kubernetes clusters, including OpenShift Virtualization environments. Disaster Recovery supports any version of Kubernetes currently supported by Trident Protect, ensuring seamless integration and robust disaster recovery capabilities for containerized applications.
To begin protecting Kubernetes-based workloads, see Kubernetes requirements for NetApp Disaster Recovery.
Resource transformations
Disaster Recovery now supports resource transformations, allowing you to modify any aspect of a workload during failover. This feature provides flexibility to adapt workloads to different environments and configurations during a disaster recovery event.
Resource transformations are applied when you create a replication plan. You can create, edit, and delete resource transformations in the new Settings page. For more information, see Manage resource transformations.
Script execution
You can now inject custom scripting into the failover workflow to coordinate the quiescence and resumption of applications. This feature helps ensure that applications are properly prepared before a snapshot is replicated and restored appropriately so operations can resume seamlessly after failover.
To learn how to inject a custom script, see Create a replication plan.
New Workloads page
Disaster Recovery has added a Workloads page to the UI, providing a comprehensive view of all discovered workloads and their protection status. The Workloads page enables you to monitor and manage your workloads more effectively.
For more information, see Review health and protection status in Disaster Recovery.
Settings page
Disaster Recovery now provides a Settings page to centrally manage resource transformation templates and AppVaults. This page provides a single interface to configure and manage these critical components of your disaster recovery plans. To learn more about options in the Settings page, see Manage resource transformations and Manage AppVaults.
General improvements
Disaster Recovery has introduced enhanced validations in the replication plan creation page to ensure a smoother, error-free user experience.
Disaster Recovery has also increased the resiliency of the service to tolerate intermittent request timeouts, enhancing the UI's overall performance and reliability.
Ransomware Resilience
Clean restore support for suspicious user behavior and user-based encryption attacks
Clean restores are now available for recovery after suspicious user behavior and user-based encryption attacks. This enhancement adds to the existing support for encryption (entropy)-based attacks. This enhanced capability enables you to take advantage of clean restore's guided approach, identifying optimal restore points to minimize data loss and accelerate recovery.
For more information, see Create an isolated recovery environment for a clean restore.
14 September 2026
Digital advisor
Deprecation notice for Virtual Machine
The Virtual Machine feature will be deprecated in Digital Advisor in October 2026.
For questions or to share feedback, contact the Active IQ team.
02 September 2026
Cloud Volumes ONTAP
Cloud Volumes ONTAP support in Azure Secret and Top Secret regions (private preview)
Cloud Volumes ONTAP now supports deployment in Azure Government Secret and Top Secret regions in private preview. This capability extends Cloud Volumes ONTAP to Microsoft's classified Azure environments, enabling government and defense customers to use ONTAP for data management, protection, and disaster recovery to support workloads for national security. Contact your NetApp accounts team to participate.
For information, refer to Azure documentation:
01 September 2026
StorageGRID
Support for StorageGRID 12.1
You can now manage your StorageGRID 12.1 system from NetApp Console.
31 August 2026
Disaster Recovery
Improved SnapMirror snapshot management
You can now trigger failover using the latest snapshot, which is the preferred method when you're not taking a new snapshot.
When selecting a specific snapshot baseline, SnapMirror transfer snapshots are hidden by default. This is because they can be deleted mid-failover, leading to an inability to reprotect the workload after failover due to a "no common snapshot found" error. You can still use these snapshots, but will have to complete an additional confirmation prompt to acknowledge the risk.
For more information, see Fail over to a remote site.
Other improvements
-
Minor improvements have been made to increase the resiliency of the test failover workflow.
-
A validation error when adding a script has been corrected.
25 August 2026
Ransomware Resilience
SIEM event delivery through the Console agent
Ransomware Resilience now supports delivering SIEM events through the Console agent, in addition to the existing option to deliver events through NetApp Console.
When you deliver SIEM events through the Console agent, you can keep SIEM event delivery within your network boundary. This simplifies deployment for on-premises environments with strict IP address allow lists and can align better with existing security controls. To use this option, ensure the Console agent can resolve and connect to your SIEM endpoint on the required port through any firewall or proxy controls.
For more information, see Configure a SIEM system.
Cloud Volumes ONTAP
Support for Austria East and Belgium Central regions in Azure
You can now deploy Cloud Volumes ONTAP 9.12.1 GA and later in the Austria East (austriaeast) and Belgium Central (belgiumcentral) regions in Azure. The following deployment types are supported:
-
Single-node
-
HA in a single availability zone using locally redundant storage (LRS)
-
HA in multiple availability zones using zone-redundant storage (ZRS)
For a list of all supported regions, refer to the Global Regions Map under Azure.