


Configuring the ONTAP SVM Data Collector


 Suggest changes

 PDFs

The ONTAP SVM Data Collector lets Workload Security monitor file and user access activity on NetApp ONTAP storage virtual machines (SVMs). The collector connects to ONTAP over HTTPS to configure FPolicy; ONTAP then connects back to the Workload Security Agent to stream file and user access events. This guide covers supported versions, prerequisites, connection methods, permissions, the Test Connection pre-check, configuration fields, feature-specific setup, and common problems with their fixes.
Recommended: For fastest, most reliable setup, connect via Cluster management IP + SVM name with cluster credentials, and run Test Connection before saving. This single practice prevents the majority of collector setup issues.
Supported versions and platforms
| Item | Support |
|---|---|
ONTAP (minimum) |
ONTAP 9.2 and later. For best performance, use ONTAP later than 9.13.1. |
SMB |
SMB 3.1 and earlier. |
NFS |
Up to and including NFS 4.1 (NFS 4.1 requires ONTAP 9.15 or later). |
FlexGroup |
ONTAP 9.4 and later. |
FlexCache (NFS) |
ONTAP 9.7 and later. |
FlexCache (SMB) |
ONTAP 9.14.1 and later. |
ONTAP Select |
Supported. |
SVM type / subtype |
Data SVMs only (no infinite volumes). Supported subtypes: default, sync_source, sync_destination. DP-destination SVMs are skipped for audit by design. |
data-fpolicy-client service policy |
Required from ONTAP 9.8 and later (see Service policy). On earlier releases it need not be set. |
Feature version floors |
Access Denied: 9.13.0+ • Autonomous Ransomware Protection (ARP) events: 9.11.1+ • Persistent Store: 9.14.1+ • Protobuf event format: 9.15+ |
Important: The data-fpolicy-client service policy is required from ONTAP 9.8 and later. On earlier releases it need not be set.
Before you begin
-
An Agent must be installed and Connected before you can run Test Connection or add a data collector. See Deploy Workload Security Agents and Agent Requirements.
-
Configure a User Directory Collector for every domain whose users access the monitored SVM. Test Connection is not available for User Directory collectors; without one, Activity Forensics shows SIDs instead of user names.
-
Reserve the required FPolicy callback ports toward the Agent. Test Connection exercises only the live ports it allocates, not the entire reserved range. Also ensure every SVM data LIF can route to the Agent; the Agent IP result selects a local address but does not test the route.
-
Configure only one collector, in one Workload Security environment, for an SVM. Test Connection does not detect a duplicate collector in another environment.
Network requirements
| Path | Port(s) | Purpose |
|---|---|---|
Agent → ONTAP (cluster or SVM management IP) |
TCP 443 |
REST/ONTAPI over HTTPS to configure FPolicy. |
ONTAP SVM data LIFs → Agent |
TCP 35000–55000 |
FPolicy file/user access events (ONTAP calls back to the Agent). |
ONTAP cluster management IP → Agent |
TCP 35000–55000 |
EMS events (for example ARP), when those features are used. |
Agent → ONTAP cluster management |
SSH 22 |
CIFS/SMB user blocking (cluster credentials). |
You do not need to open the entire 35000–55000 range. Each SVM uses up to 4 ports (2 per enabled protocol — NFS and CIFS/SMB); reserve about 200 ports for a fully loaded Agent (50 collectors). Open the range toward the Agent, including any firewall on the Agent host itself.
Note: When a firewall is enabled, define an exception for the ports used by the collector. When the Agent runs in AWS to monitor a Cloud ONTAP SVM, the Agent and storage must be in the same VPC, or have a valid route between VPCs.
Choose a connection method
Add an SVM using one of two methods. Cluster IP + SVM name is strongly recommended.
| Method | Credentials | What you get | Notes |
|---|---|---|---|
Cluster management IP + SVM name (recommended) |
Cluster-admin, or csuser, or an AD user with a csrole-equivalent role |
Full functionality, including Test Connection feature/RBAC checks and EMS-based features (ARP). |
SVM name must match ONTAP exactly (case-sensitive). |
SVM management IP |
vsadmin, or csuser, or an AD user with a csrole-equivalent role |
Core auditing. Test Connection cannot run feature/RBAC checks in SVM mode (the SVM account lacks the permission to run them). |
Use a dedicated SVM management LIF, or set the data LIF firewall-policy to mgmt (below). |
Common pitfall: When you connect via SVM IP with vsadmin and the LIF has a combined Data + Management role, ping works but SSH does not. Create an SVM management-only LIF, or set the data LIF firewall-policy to mgmt.
If you use SVM management IP
Cluster management IP + SVM name is recommended. If you must use SVM mode, complete this setup before Test Connection:
Set and unlock the vsadmin password for external access:
security login password -username vsadmin -vserver ++<++svmname++>++

security login unlock -username vsadmin -vserver ++<++svmname++>++
Use a dedicated SVM management LIF. If one is not available, set the data LIF firewall policy to mgmt:
network interface modify -lif ++<++SVM++_++data++_++LIF++_++name++>++ -firewall-policy mgmt

Important: SVM mode cannot run the feature and RBAC checks. Use Cluster management IP + SVM name whenever possible.
Permissions (RBAC)
Test Connection runs with the ONTAP account entered in the collector form. Before you run it, use cluster-admin credentials or create csuser/csrole with the required privileges below. Without these privileges, Test Connection cannot validate or configure FPolicy and the selected features.
Minimum privileges by capability
| Capability | Required privilege(s) | ONTAP floor |
|---|---|---|
FPolicy (required for all deployments) |
vserver fpolicy: all |
Any supported |
Administrator shortcut |
role DEFAULT: readonly (cluster) — satisfies read checks; fpolicy still needs all |
— |
Snapshots |
volume snapshot: all (scope to cloudsecure_* where possible) |
Any |
EMS-based monitoring |
event catalog, event filter, event notification, event notification destination, security certificate: all |
Any |
ONTAP Access Denied |
REST access + vserver fpolicy events |
9.13.0+ |
Autonomous Ransomware Protection (ARP) events |
security anti-ransomware volume + volume: readonly/all |
9.11.1+ |
Persistent Store |
vserver fpolicy: all + job show: readonly (or all) |
9.14.1+ |
Protobuf event format |
vserver fpolicy: all |
9.15+ |
User Access Blocking (SMB & NFS) |
SSH (application ssh + port 22) + set: all, and vserver export-policy rule, vserver cifs session, vserver services access-check authentication translate, vserver name-mapping: all. Cluster credentials only. |
Any |
Common pitfall: For AD-backed ONTAP accounts, grant the role to the user directly. If the role is assigned only at the group level, the permission probe cannot read it and Test Connection reports "Roles assigned at the group level instead of the user level for this Active Directory user."
Create csuser via Cluster management IP
If an existing csuser/csrole must be replaced first:
security login delete -user-or-group-name csuser -application ++*++
security login role delete -role csrole -cmddirname ++*++
security login rest-role delete -role csrestrole -api ++*++
security login rest-role delete -role arwrole -api ++*++
Create the role and user (run as cluster administrator):
security login role create -role csrole -cmddirname DEFAULT -access readonly
security login role create -role csrole -cmddirname "vserver fpolicy" -access all
security login role create -role csrole -cmddirname "volume snapshot" -access all -query "-snapshot cloudsecure++_*++"
security login role create -role csrole -cmddirname "event catalog" -access all
security login role create -role csrole -cmddirname "event filter" -access all
security login role create -role csrole -cmddirname "event notification destination" -access all
security login role create -role csrole -cmddirname "event notification" -access all
security login role create -role csrole -cmddirname "security certificate" -access all
security login role create -role csrole -cmddirname "cluster application-record" -access all
security login create -user-or-group-name csuser -application ontapi -authmethod password -role csrole
security login create -user-or-group-name csuser -application ssh -authmethod password -role csrole
security login create -user-or-group-name csuser -application http -authmethod password -role csrole
Create csuser via SVM (Vserver) management IP
If an existing csuser/csrole must be replaced first:
security login delete -user-or-group-name csuser -application ++*++ -vserver ++<++vservername++>++
security login role delete -role csrole -cmddirname ++*++ -vserver ++<++vservername++>++
security login rest-role delete -role csrestrole -api ++*++ -vserver ++<++vservername++>++
Create the role and user (replace <vservername> before running):
security login role create -vserver ++<++vservername++>++ -role csrole -cmddirname DEFAULT -access none
security login role create -vserver ++<++vservername++>++ -role csrole -cmddirname "network interface" -access readonly
security login role create -vserver ++<++vservername++>++ -role csrole -cmddirname version -access readonly
security login role create -vserver ++<++vservername++>++ -role csrole -cmddirname volume -access readonly
security login role create -vserver ++<++vservername++>++ -role csrole -cmddirname vserver -access readonly
security login role create -vserver ++<++vservername++>++ -role csrole -cmddirname "vserver fpolicy" -access all
security login role create -vserver ++<++vservername++>++ -role csrole -cmddirname "volume snapshot" -access all
security login create -user-or-group-name csuser -application ontapi -authmethod password -role csrole -vserver ++<++vservername++>++
security login create -user-or-group-name csuser -application http -authmethod password -role csrole -vserver ++<++vservername++>++
Feature-specific permissions
Persistent Store (cluster mode shown; add -vserver <vservername> for SVM mode):
security login role create -role csrole -cmddirname "vserver fpolicy" -access all
security login role create -role csrole -cmddirname "job show" -access readonly
Protobuf (cluster mode shown; add -vserver <vservername> for SVM mode):
security login role create -role csrole -cmddirname "vserver fpolicy" -access all
For Access Denied and ARP, cluster administrator credentials need no extra permissions. For a custom user, add the privileges in the capability table above. See the ONTAP Access Denied and ONTAP Autonomous Ransomware Protection integration guides.
Configure and test the data collector
-
Log in as Administrator or Account Owner to Data Infrastructure Insights.
-
Select Workload Security > Collectors > +Data Collectors.
-
Hover over the NetApp SVM tile and click +Monitor.
-
Enter the fields below. Do not save the collector yet.
| Field | Description |
|---|---|
Name |
Unique name for the data collector. |
Agent |
Select a configured, Connected Agent. |
Connect via Management IP for |
Choose Cluster IP (recommended) or SVM Management IP. |
Cluster / SVM Management IP Address |
Management IP for the cluster or SVM, per your selection. |
SVM Name |
The SVM name (required when connecting via Cluster IP). Must match ONTAP exactly (case-sensitive). |
Username |
Cluster IP: cluster-admin, csuser, or AD user with csrole-equivalent. SVM IP: vsadmin, csuser, or AD user with csrole-equivalent. |
Password |
Password for the account above. |
Filter Shares/Volumes |
Choose to include or exclude specific shares/volumes from event collection. |
Share names to include/exclude |
Comma-separated complete share names (no quotes). For long lists, filter by volume instead of share. |
Volume names to include/exclude |
Comma-separated complete volume names (no quotes). |
Monitor Folder Access |
Enables general folder-access events. Folder create/rename/delete are captured even without this option. Enabling increases event volume. |
Set ONTAP Send Buffer size |
Tunes the FPolicy send buffer. On ONTAP prior to 9.8p7 with performance issues, adjust to improve ONTAP performance. Contact NetApp Support if the option is not shown. |
Important: Default excluded file extensions: by design, Workload Security configures the FPolicy scope to exclude the ini and DS_Store extensions. Events for these files are filtered on ONTAP and never reach Workload Security, so they do not appear in Activity Forensics. This is separate from customer-configurable alerting exclusions. It is expected behavior; auditing these extensions is not configurable in the UI.
Run Test Connection before saving
The Test Connection feature (introduced March 2025) validates connectivity, credentials, data LIFs, the FPolicy callback, and per-feature RBAC before you create the collector, so you can self-correct network and permission issues. On the add/edit collector page, enter the details and click Test Connection.
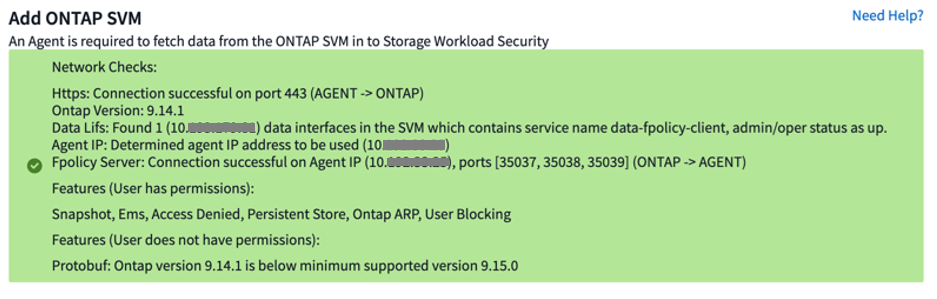
Example of a successful Test Connection result.
Run it via Cluster management IP + SVM name with cluster credentials for full coverage.
| Check | What it confirms | If it fails |
|---|---|---|
Https |
Agent can reach ONTAP management on TCP 443. |
Check IP/mode and 443 firewall. |
Ontap Version |
Credentials work; version and feature eligibility. |
Check credentials/RBAC and ONTAP version. |
Data Lifs |
A usable data LIF exists with data-fpolicy-client (9.8+), up. |
Add data-fpolicy-client to the service policy (see Service policy). |
Agent IP |
The Agent has an active local address in the same IPv4 or IPv6 family as the SVM data LIFs. It does not prove routing. |
Ensure the Agent has an eligible local address. If Fpolicy Server later fails, verify routing from each SVM data LIF to the Agent. |
Fpolicy Server |
ONTAP can call back to the Agent and complete the FPolicy handshake on live ports. |
Open 35000–55000 toward the Agent; verify one-SVM-one-collector. |
Features |
Per-feature RBAC and ONTAP-version eligibility (cluster mode only). |
Grant the missing privileges (see Permissions). |
Important*: Limitations: Test Connection tests only a subset of the 35000–55000 ports (keep the full reserved range open). The Agent IP result selects an active local address in the same IPv4 or IPv6 family as the data LIFs; it does not test routing from each data LIF to the Agent. Test Connection also does not generate or validate real file-event flow. Feature/RBAC checks do not run in SVM mode because the SVM account lacks the required permission, and Test Connection is not available for User Directory collectors.
When all four network checks pass, review the feature results for every feature you plan to use, then save the collector.
Important: Test Connection SUCCESS is based on the four network checks. Feature results are informational, so SUCCESS does not mean that every optional feature has the required RBAC. Correct failed feature checks before enabling those features.
If the Data Lifs check fails
Do not verify the data LIF manually before Test Connection. If the Data Lifs result fails, use the following commands to correct the service policy. From ONTAP 9.8 and later, at least one operational SVM data LIF must include data-fpolicy-client with data-nfs and/or data-cifs:
net int service-policy create -policy only++_++data++_++fpolicy -vserver ++<++svm++>++ ++\++ \
-allowed-addresses 0.0.0.0/0 -services data-cifs,data-nfs,data,-core,data-fpolicy-client
Verify the LIF:
network interface show -vserver ++<++svm++>++ -fields service-policy,status-admin,status-oper
On ONTAP prior to 9.8, data-fpolicy-client need not be set; a LIF with role data (up) carrying NFS and/or CIFS is sufficient.
Feature setup
Multi-Admin Verify (MAV)
If MAV is enabled, it can block the commands Workload Security uses for snapshots and user blocking. Add exclusions:
multi-admin-verify rule modify -operation "volume snapshot create" -query "-snapshot !++*++cloudsecure++_*++"
multi-admin-verify rule modify -operation "volume snapshot delete" -query "-snapshot !++*++cloudsecure++_*++"
multi-admin-verify rule delete -operation set # allow user blocking
User Access Blocking (SMB & NFS)
-
Requires cluster-level credentials (SMB blocks the user; NFS blocks the host IP). With cluster-admin, no extra permissions are needed — just ensure SSH (port 22) to cluster management.
-
With a custom user (csuser), grant the cluster-level privileges below, ensure the user can SSH, then restart the ONTAP and User Directory collectors.
security login role create -role csrole -cmddirname "vserver export-policy rule" -access all
security login role create -role csrole -cmddirname set -access all
security login role create -role csrole -cmddirname "vserver cifs session" -access all
security login role create -role csrole -cmddirname "vserver services access-check authentication translate" -access all
security login role create -role csrole -cmddirname "vserver name-mapping" -access all
Persistent Store
Supported from ONTAP 9.14.1. Enable it with the checkbox on the add/edit page and provide a volume name (mandatory). Behavior differs by version:
-
ONTAP 9.14.1: create the volume yourself (16 GB recommended) and enter its name.
-
ONTAP 9.15.1: the collector auto-creates a 16 GB volume using the name you provide.
Requires vserver fpolicy: all plus job show: readonly (see Feature-specific permissions).
Protobuf mode
When enabled in Advanced Configuration, Workload Security configures the FPolicy engine in protobuf mode. Supported from ONTAP 9.15. Requires vserver fpolicy: all. See the ONTAP documentation for details.
Recommended configuration for MetroCluster
-
Configure two collectors: one to the source SVM and one to the destination SVM.
-
Connect both by Cluster IP.
-
At any time the active SVM’s collector shows Running and the standby shows Stopped.
-
On switchover, the states swap; allow up to two minutes for the transition.
Note: A Stopped MetroCluster collector on the standby side is expected, not an error. Investigate only if the active side is not Running.
Pause and resume a collector
Pause and Resume apply to a data collector, not to an Agent. You can run them from the UI (Collectors > the collector > options menu) or from the API.
Pausing a Running collector removes FPolicy configuration from ONTAP. While paused, no events flow, and no data is sent in either direction.
-
New volumes created while paused are not picked up until you resume.
-
Snapshot purge does not run on a paused collector.
-
EMS events (such as ONTAP ARP) are not processed while paused — file-tampering events can be missed.
-
Health notification emails are not sent for a paused collector.
-
Manual or automatic actions (snapshot, user blocking) are not supported while paused.
-
A paused collector stays paused across agent/collector upgrades and agent restarts/reboots.
-
A collector in Error state cannot be paused; Pause is enabled only from Running.
-
If the Agent is disconnected, the collector goes to Stopped and Pause is disabled.
When to use Pause
-
Use Pause for extended ONTAP-side maintenance, such as a planned ONTAP upgrade or an SVM outage, so that FPolicy configuration is removed cleanly while the storage is unavailable.
-
Resume as soon as maintenance is complete. Activity that occurs while a collector is paused is not collected.
-
Do not use Pause to control when an Agent or a collector upgrades. Pin and unpin the Agent instead (see Deploy Workload Security Agents).
Note: A collector cannot be paused while it has restricted (blocked) users. Restore user access first.
Migrate a collector to another Agent
You can move a collector between Agents to balance load.
-
Source Agent must be Connected; the collector must be Running.
-
Supported for both Data and User Directory collectors; not supported for manually managed tenants.
-
Edit the collector, choose a destination Agent, and click Save Collector. Configuration changes on the edit page are retained after a successful migration.
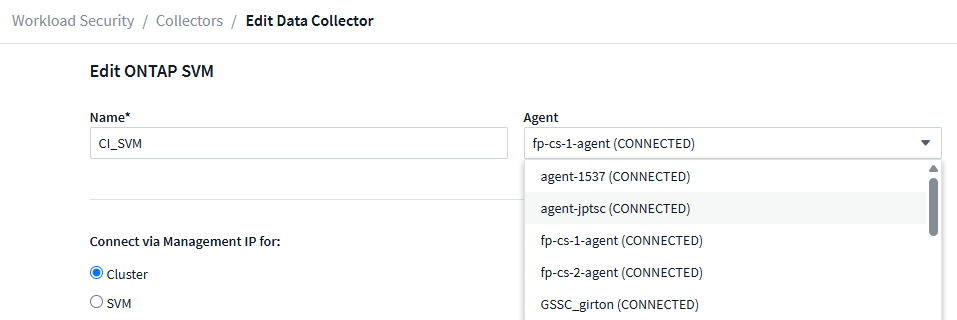
Select another Agent to migrate the collector.
Best practices for data collectors
-
Run Test Connection before you save a collector, and resolve every failed check. Most collector errors are unmet prerequisites that Test Connection detects.
-
Connect via Cluster management IP with the SVM name and cluster credentials. SVM mode cannot run the feature and RBAC checks.
-
Configure one collector per SVM, in one Workload Security environment only. A second collector replaces the FPolicy destination of the first.
-
Configure a User Directory Collector for every domain whose users access the monitored SVMs, before or with the first ONTAP SVM collector, so that activity shows user names instead of SIDs.
-
Enter complete share and volume names without quotation marks. For long lists, filter by volume rather than by share.
-
Enable Monitor Folder Access only when you need general folder-access events, because it increases event volume.
-
Keep the hosting Agent within capacity — at most 50 collectors, within a ceiling of 20,000 events per second — and use the Event Rate Checker to size for peak event rate.
-
For MetroCluster, configure one collector for the source SVM and one for the destination SVM, both connected by Cluster IP.
-
Use Pause only for extended ONTAP-side maintenance. To control when upgrades happen, pin and unpin the Agent (see Deploy Workload Security Agents).
-
For best FPolicy performance, place the Agent close to the storage network and minimize network latency.
If the collector reports an error after saving
Test Connection covers setup-time connectivity, credentials, data LIFs, callback connectivity on allocated ports, the CIFS server check when SMB is selected, and feature access in Cluster mode. Do not repeat those checks manually after a successful test.
If the collector later enters Error or Degraded state, open Status > More detail and follow Troubleshooting the ONTAP SVM Data Collector. Runtime conditions such as duplicate collectors, event-rate overload, paused collectors, Persistent Store placement, MetroCluster transitions, missing activity, and identity resolution are outside the pre-save Test Connection workflow.
After you finish
-
On the Installed Data Collectors page, use the options menu to edit or restart a collector.
-
Confirm the collector reaches Running and that events appear in Workload Security > Activity Forensics after real client I/O.
-
Verify usernames resolve (not SIDs); if not, check the User Directory Collector.